
Featured Articles:

Webinar: False Claims Act Enforcement Update: Healthcare, Defense and Tariff Evasion

Webinar: December 2, 2026 12 Noon EST Sign Up HERE The False Claims Act has become the government’s most powerful civil fraud weapon, and enforcement has never been more aggressive. DOJ reported record FCA recoveries for fiscal year 2025, whistleblowers filed a record number of qui tam suits, and DOJ’s Trade Fraud Task Force has turned the FCA into a primary tool for pursuing tariff...
Episode 464 — Responsible AI Use

Michael Volkov examines why every organization needs a responsible AI use policy now, as employees adopt AI tools faster than companies can govern them. Drawing on court sanctions against lawyers for AI-fabricated citations, SEC “AI washing” enforcement actions, and data leaks into public chatbots, Michael explains that these failures stem from weak governance rather than weak technology. He highlights DOJ’s Evaluation of Corporate Compliance Programs,...

Fund It, Find It, Tell Us: What DOJ’s Criminal Division Chief Told the C-Suite About Compliance and Self-Disclosure

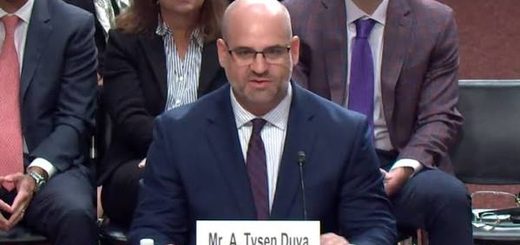
At a third-party risk management and supply chain conference in Chicago on Wednesday, October 28, 2026, Assistant Attorney General A. Tysen Duva, who has led the Justice Department’s Criminal Division since December 2025, delivered a message aimed squarely at boards and chief executives: fund compliance properly, and when it finds something, come to the Department early. The remarks, made in a fireside chat and reported...

Penny Wise, Pound Foolish: Why Compliance Is Not a Cost Center (III of III)

When budgets tighten, compliance is often among the first functions to feel the squeeze. The pitch is familiar: it produces no revenue, the enforcement environment has eased, and a leaner team can do the same work with better tools. Some of those points have a grain of truth. Technology can make compliance more efficient. But the underlying premise, that compliance is overhead to be minimized,...

Reallocation, Not Retreat: Why Lower FCPA Priority Does Not Mean Lower Corporate Risk (Part II of III)

A dangerous misreading has taken hold in many boardrooms. Because the current administration paused and narrowed Foreign Corrupt Practices Act enforcement, the argument goes, enforcement risk in general has dropped, and compliance spending can drop with it. That reasoning confuses one statute with the whole landscape. The administration has not stopped enforcing the law. It has reassigned enforcement resources toward priorities defined by national security...

Are Your Import Declarations Accurate?

Lying about where your goods come from is now one of the most expensive mistakes in trade compliance. DOJ stood up a dedicated trade fraud task force in August of last year, and it moved fast. Its first settlement came three months later. This May, it announced the largest customs-related False Claims Act recovery ever, roughly $550 million from aluminum companies and affiliated warehouses accused...

Compliance Without Stature: What Bank of America Teaches Us About the Retrenchment of Compliance (Part I of III)

Across corporate America, a quiet retrenchment is under way. Compliance budgets are being flattened or trimmed, headcount is being “optimized,” chief compliance officers are being moved further from the executive suite, and programs built over a decade are being described as overhead to be right-sized. The justification is usually the same: the enforcement climate has changed, so the risk has changed. The Bank of America...

Can a Cybersecurity Certification Trigger FCA Liability?

You don’t need a data breach to commit False Claims Act fraud. You just need a cybersecurity certification that isn’t true. Honeywell Aerospace just paid more than $2 million to resolve allegations that, from April 2020 through December 2023, it billed on a Defense Department contract while failing to meet the cybersecurity standard known as NIST SP 800-171, the standard for protecting controlled unclassified information....

Remediation, Cooperation, and What Every Compliance Program Should Take From the Bank of America Penalties (Part V of V)

The first four posts in this series described what went wrong. This one asks what Bank of America is required to do now, how its cooperation and remediation were treated, and what a compliance officer at any institution should do on Monday morning. What the Bank Must Do Under the FinCEN consent order, the bank must work with a third party to complete a lookback...

475 Apparent Violations: OFAC’s $11.66 Million Case Against Bank of America and the Limits of Screening (Part IV of V)

On the same day that FinCEN and the OCC announced their penalties, OFAC announced its own: $11,662,930 for 475 apparent violations arising from sanctions screening failures between September 18, 2021 and April 24, 2025. The total value of the apparent violations was approximately $14.8 million. For a bank of this size, the dollar amount is modest. What makes the case important is the base penalty...